

TrueNAS Development Documentation
This content follows experimental development changes in TrueNAS 27, a future version of TrueNAS.
Use the Product and Version selectors above to view content specific to a stable software release.
NFS Services Screen
4 minute read.
The System > Services screen includes two options on the NFS service row:
- View Sessions opens the NFS Sessions screen.
- Configure icon opens the NFS Service screen.
The UDP protocol is deprecated and not supported with NFS. It is disabled by default in the Linux kernel. Using UDP over NFS on modern networks (1Gb+) can lead to data corruption caused by fragmentation during high loads.
The Services > NFS configuration screen displays settings to customize the TrueNAS NFS service.
You can access it from System > Services screen. Locate NFS and click edit to open the screen, or use the Config Service option on the Unix (NFS) Share widget options menu found on the main Sharing screen.
Select Start Automatically to activate the NFS service when TrueNAS boots.
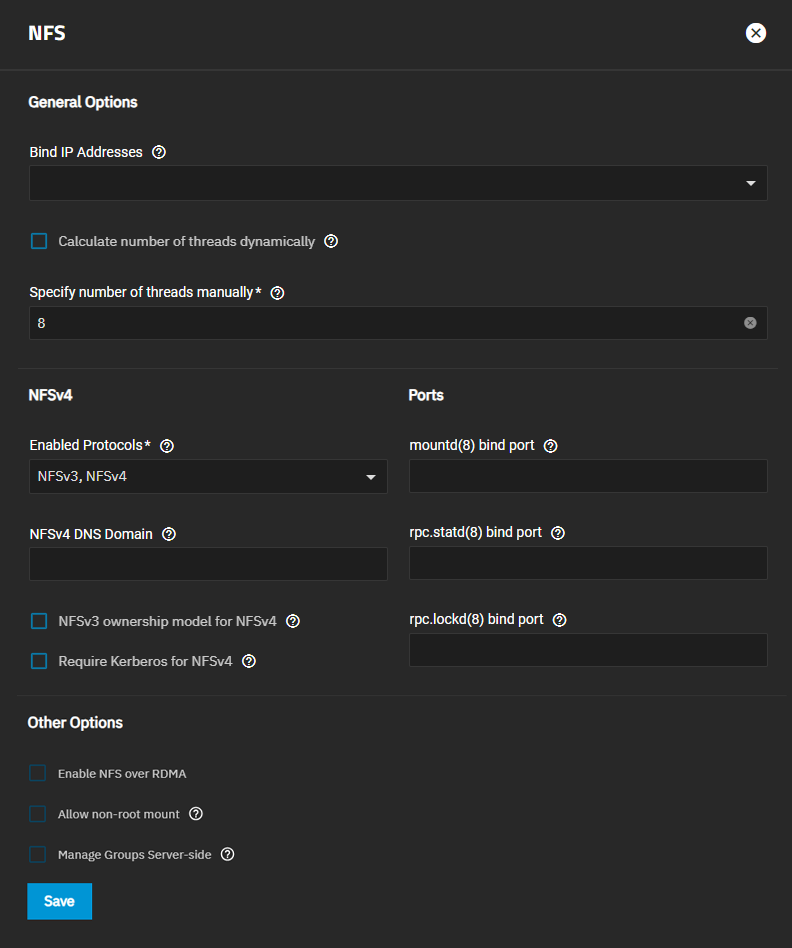
| Setting | Description |
|---|---|
| Bind IP Addresses | Sets the IP addresses the share (SMB or NFS) listens on. Leaving empty listens on all available addresses. Must configure static IPs on the interface to show one the list. |
| Calculate number of threads dynamically | Automatically sets the number of threads used by the kernel NFS server. |
| Specify number of threads manually | Sets the optimal thread count for the kernel NFS server. Shows after disabling Calculate number of threads dynamically. |
| Setting | Description |
|---|---|
| Enabled Protocols | Sets the NFS service protocol to NFSv3, NFSv4, or both. When NFSv4 is selected, NFSv3 ownership model for NFSv4 clears, allowing you to select or leave it clear. |
| NFSv4 DNS Domain | Overrides the default DNS domain for NFSv4. Specifies the domain in idmapd.conf. Select to use a value to override the default DNS domain name for NFSv4. When AD is joined and healthy, NFSv4 is selected as an enabled protocol, setting this shows Add SPN to the right of Save. |
| NFSv3 ownership model for NFSv4 | Enables NFSv4 ACL support without requiring the client and the server to sync users and groups. Becomes selectable after selecting NFSv4. Deactivates Manage Groups Server-side. |
| Require Kerberos for NFSv4 | Forces NFS shares to fail if a Kerberos ticket is unavailable. |
ADD SPN only shows on the NFS service screen when AD is joined and hhealty, NFSv4 is selected in Enabled Protocols, and Require Kerberos for NFSv4 is enabled. After saving settings and reopening the NFS service screen, the Add SPN button becomes active. Clicking this opens the first Add Kerberos SPN Entry dialog. Clicking Yes in the fist dialog opens the second Add Kerberos SPN Entry dialog where you add the credentials.
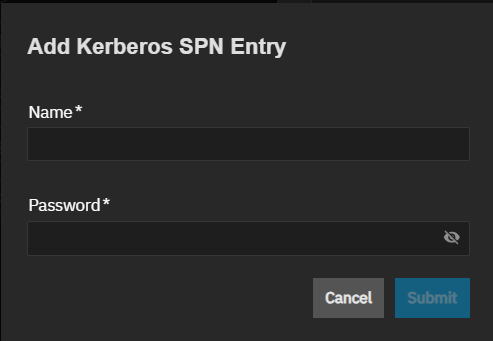
| Setting | Description |
|---|---|
| Name | Specifies the AD admin account credential name with the rights to create SPNs in the domain, commonly a domain admin for delegated account granted write servicePrincipalName permissions on the relevant computer object. This is not the TrueNAS administrator account name. |
| Password | Specifies crendtial password for the AD admin account as mentioned in Name. |
| Setting | Description |
|---|---|
| mountd(8) bind port | Specifies a port to bind mountd(8). |
| rpc.statd(8) bind port | Specifies a port to bind rpc.statd(8). |
| rpc.lockd(8) bind port | Specifies a port to bind rpc.lockd(8). |
| Setting | Description |
|---|---|
| Enable NFS over RDMA | Improves NFS performance and reduce CPU overhead. This setting requires an Enterprise licensed system with an RDMA capable NIC. |
| Allow non-root mount | Allows serving non-root mount requests. Only enable if required by the NFS client. |
| Manage Groups Server-side | Allows the server to determine group IDs via server-side lookups instead of client-provided information. Supports more than 16 groups and provides more accurate memberships. Equivalent to the --manage-gids flag for rpc.mountd. |
Changes to local groups or directory service groups take up to 10 minutes to take effect for NFS shares. For immediate effect, reload or restart the NFS service.
We recommend using the default NFS settings unless you require specific settings. When TrueNAS is already connected to Active Directory, setting NFSv4 and Require Kerberos for NFSv4 also requires a Kerberos Keytab.